EC-Council Certified CISO (CCISO) Practice Test


Exam Name EC-Council Certified Chief Information Security Officer (CCISO)
Exam Code 712-50
Duration 150 mins
Number of Questions 150
Passing Score 72%
Governance and Risk Management
1. Define- Implement- Manage- and Maintain an Information Security Governance Program
- Form of Business Organization
- Industry
- Organizational Maturity
2. Information Security Drivers
3. Establishing an information security management structure
- Organizational Structure
- Where does the CISO fit within the organizational structure
- The Executive CISO
- Nonexecutive CISO
4. Laws/Regulations/Standards as drivers of Organizational Policy/Standards/Procedures
5. Managing an enterprise information security compliance program
- Security Policy
Necessity of a Security Policy
Security Policy Challenges
- Policy Content
Types of Policies
Policy Implementation
- Reporting Structure
- Standards and best practices
- Leadership and Ethics
- EC-Council Code of Ethics
6. Introduction to Risk Management
- Organizational Structure
- Where does the CISO fit within the organizational structure
- The Executive CISO
- Nonexecutive CISO
Information Security Controls- Compliance- and Audit Management
1. Information Security Controls
- Identifying the Organizations Information Security Needs
Identifying the Optimum Information Security Framework
Designing Security Controls
Control Lifecycle Management
Control Classification
Control Selection and Implementation
Control Catalog
Control Maturity
Monitoring Security Controls
Remediating Control Deficiencies
Maintaining Security Controls
Reporting Controls
Information Security Service Catalog
2. Compliance Management
- Acts- Laws- and Statutes
FISMA
- Regulations
GDPR
- Standards
ASD - Information Security Manual
Basel III
FFIEC
ISO 00 Family of Standards
NERC-CIP
PCI DSS
NIST Special Publications
Statement on Standards for Attestation Engagements No. 16 (SSAE 16)
3. Guidelines- Good and Best Practices
- CIS
OWASP
4. Audit Management
- Audit Expectations and Outcomes
- IS Audit Practices
ISO/IEC Audit Guidance
Internal versus External Audits
Partnering with the Audit Organization
Audit Process
General Audit Standards
Compliance-Based Audits
Risk-Based Audits
Managing and Protecting Audit Documentation
Performing an Audit
Evaluating Audit Results and Report
Remediating Audit Findings
Leverage GRC Software to Support Audits
5. Summary
Security Program Management & Operations
1. Program Management
- Defining a Security Charter- Objectives- Requirements- Stakeholders- and Strategies
Security Program Charter
Security Program Objectives
Security Program Requirements
Security Program Stakeholders
Security Program Strategy Development
- Executing an Information Security Program
- Defining and Developing- Managing and Monitoring the Information Security Program
Defining an Information Security Program Budget
Developing an Information Security Program Budget
Managing an Information Security Program Budget
Monitoring an Information Security Program Budget
- Defining and Developing Information Security Program Staffing Requirements
- Managing the People of a Security Program
Resolving Personnel and Teamwork Issues
Managing Training and Certification of Security Team Members
Clearly Defined Career Pat
Designing and Implementing a User Awareness Program
- Managing the Architecture and Roadmap of the Security Program
Information Security Program Architecture
Information Security Program Roadmap
- Program Management and Governance
Understanding Project Management Practices
Identifying and Managing Project Stakeholders
Measuring the Effectives of Projects
- Business Continuity Management (BCM) and Disaster Recovery Planning (DRP)
- Data Backup and Recovery
- Backup Strategy
- ISO BCM Standards
Business Continuity Management (BCM)
Disaster Recovery Planning (DRP)
- Continuity of Security Operations
Integrating the Confidentiality- Integrity and Availability (CIA) Model
- BCM Plan Testing
- DRP Testing
- Computer Incident Response
Incident Response Tools
Incident Response ManagementIncident Response Communications
Post-Incident Analysis
Testing Incident Response Procedures
- Digital Forensics
Crisis Management
Digital Forensics Life Cycle
2. Operations Management
- Establishing and Operating a Security Operations (SecOps) Capability
- Security Monitoring and Security Information and Event Management (SIEM)
- Event Management
- Incident Response Model
Developing Specific Incident Response Scenarios
- Threat Management
- Threat Intelligence
Information Sharing and Analysis Centers (ISAC)
- Vulnerability ManagementThreat Hunting
Vulnerability Assessments
Vulnerability Management in Practice
Penetration Testing
Security Testing Teams
Remediation
3. Summary
Information Security Core Competencies
1. Access Control
- Authentication- Authorization- and Auditing
- Authentication
- Authorization
- Auditing
- User Access Control Restrictions
- User Access Behavior Management
- Types of Access Control Models
- Designing an Access Control Plan
- Access Administration
2. Physical Security
- Designing- Implementing- and Managing Physical Security Program
Physical Risk Assessment
- Physical Location Considerations
- Obstacles and Prevention
- Secure Facility Design
Security Operations Center
Sensitive Compartmented Information Facility
Digital Forensics Lab
Datacenter
- Preparing for Physical Security Audits
3. Network Security
- Network Security Assessments and Planning
- Network Security Architecture Challenges
- Network Security Design
- Network Standards- Protocols- and Controls
Network Security Standards
Protocols
4. Certified Chief
- Network Security Controls
- Wireless (Wi-Fi) Security
Wireless Risks
Wireless Controls
- Voice over IP Security
5. Endpoint Protection
- Endpoint Threats
- Endpoint Vulnerabilities
- End User Security Awareness
- Endpoint Device Hardening
- Endpoint Device Logging
- Mobile Device Security
Mobile Device Risks
Mobile Device Security Controls
- Internet of Things Security (IoT)
Internet of Things Security (IoT)
6. Application Security
- Secure SDLC Model
- Separation of Development- Test- and Production Environments
- Application Security Testing Approaches
- DevSecOps
- Waterfall Methodology and Security
- Agile Methodology and Security
- Other Application Development Approaches
- Application Hardening
- Application Security Technologies
- Version Control and Patch Management
- Database Security
- Database Hardening
- Secure Coding Practices
7. Encryption Technologies
- Encryption and Decryption
- Cryptosystems
Blockchain
Digital Signatures and Certificates
PKI
Key Management
- Hashing
- Encryption Algorithms
- Encryption Strategy Development
Determining Critical Data Location and Type
Deciding What to Encrypt
Determining Encryption Requirements
Selecting- Integrating- and Managing Encryption Technologies
8. Virtualization Security
- Virtualization Overview
- Virtualization Risks
- Virtualization Security Concerns
- Virtualization Security Controls
- Virtualization Security Reference Model
9. Cloud Computing Security
- Overview of Cloud Computing
- Security and Resiliency Cloud Services
- Cloud Security Concerns
- Cloud Security Controls
- Cloud Computing Protection Considerations
10. Transformative Technologies
- Artificial Intelligence
- Augmented Reality
- Autonomous SOC
- Dynamic Deception
- Software-Defined Cybersecurity
11. Summary
Strategic Planning- Finance- Procurement- and Vendor Management
1. Strategic Planning
- Understanding the Organization
Understanding the Business Structure
Determining and Aligning Business and Information Security Goals
Identifying Key Sponsors- Stakeholders- and Influencers
Understanding Organizational Financials
- Creating an Information Security Strategic Plan
Strategic Planning Basics
Alignment to Organizational Strategy and Goals
Defining Tactical Short- Medium- and Long-Term Information Security Goals
Information Security Strategy Communication
Creating a Culture of Security
2. Designing- Developing- and Maintaining an Enterprise Information Security Program
- Ensuring a Sound Program Foundation
- Architectural Views
- Creating Measurements and Metrics
- Balanced Scorecard
- Continuous Monitoring and Reporting Outcomes
- Continuous Improvement
- Information Technology Infrastructure Library (ITIL) Continual Service Improvement (CSI)
3. Understanding the Enterprise Architecture (EA)
- EA Types
The Zachman Framework
The Open Group Architecture Framework (TOGAF)
Sherwood Applied Business Security Architecture (SABSA)
Federal Enterprise Architecture Framework (FEAF)
4. Finance
- Understanding Security Program Funding
- Analyzing- Forecasting- and Developing a Security Budget
Resource Requirements
Define Financial Metrics
Technology Refresh
New Project Funding
Contingency Funding
- Managing the information Security Budget
Obtain Financial Resources
Allocate Financial Resources
Monitor and Oversight of Information Security Budget
Report Metrics to Sponsors and Stakeholders
Balancing the Information Security Budget
5. Procurement
- Procurement Program Terms and Concepts
Statement of Objectives (SOO)
Statement of Work (SOW)
Total Cost of Ownership (TCO)
Request for Information (RFI)
Request for Proposal (RFP)
Master Service Agreement (MSA)
Service Level Agreement (SLA)
Terms and Conditions (T&C)
- Understanding the Organizations Procurement Program
Internal Policies- Processes- and Requirements
External or Regulatory Requirements
Local Versus Global Requirements
- Procurement Risk Management
Standard Contract Language
6. Vendor Management
- Understanding the Organizations Acquisition Policies and Procedures
Procurement Life cycle
- Applying Cost-Benefit Analysis (CBA) During the Procurement Process5
- Vendor Management Policies
- Contract Administration Policies
Service and Contract Delivery Metrics
Contract Delivery Reporting
Change Requests
Contract Renewal
Contract Closure
- Delivery Assurance
Validation of Meeting Contractual Requirements
Formal Delivery Audits
Periodic Random Delivery Audits
Third-Party Attestation Services (TPRM)

712-50 MCQs
712-50 TestPrep
712-50 Study Guide
712-50 Practice Test
712-50 Exam Questions
killexams.com
EC-Council
712-50
EC-Council Certified CISO (CCISO)
https://killexams.com/pass4sure/exam-detail/712-50
QUESTION: 330
Scenario: You are the newly hired Chief Information Security Officer for a company
that has not previously had a senior level security practitioner. The company lacks a
defined security policy and framework for their Information Security Program. Your
new boss, the Chief Financial Officer, has asked you to draft an outline of a security
policy and recommend an industry/sector neutral information security control
framework for implementation. Which of the following industry / sector neutral
information security control frameworks should you recommend for implementation?
A. National Institute of Standards and Technology (NIST) Special Publication 800-53
B. Payment Card Industry Digital Security Standard (PCI DSS)
C. International Organization for Standardization � ISO 27001/2
D. British Standard 7799 (BS7799)
Answer: C
QUESTION: 331
Scenario: You are the CISO and have just completed your first risk assessment for
your organization. You find many risks with no security controls, and some risks with
inadequate controls. You assign work to your staff to create or adjust existing security
controls to ensure they are adequate for risk mitigation needs. You have identified
potential solutions for all of your risks that do not have security controls. What is the
NEXT step?
A. Get approval from the board of directors
B. Screen potential vendor solutions
C. Verify that the cost of mitigation is less than the risk
D. Create a risk metrics for all unmitigated risks
Answer: C
QUESTION: 332
Access Control lists (ACLs), Firewalls, and Intrusion Prevention Systems are
examples of
A. Network based security preventative controls
B. Software segmentation controls
C. Network based security detective controls
D. User segmentation controls
105
Answer: A
QUESTION: 333
Scenario: You are the newly hired Chief Information Security Officer for a company
that has not previously had a senior level security practitioner. The company lacks a
defined security policy and framework for their Information Security Program. Your
new boss, the Chief Financial Officer, has asked you to draft an outline of a security
policy and recommend an industry/sector neutral information security control
framework for implementation. Your Corporate Information Security Policy should
include which of the following?
A. Information security theory
B. Roles and responsibilities
C. Incident response contacts
D. Desktop configuration standards
Answer: B
QUESTION: 334
Scenario: You are the CISO and have just completed your first risk assessment for
your organization. You find many risks with no security controls, and some risks with
inadequate controls. You assign work to your staff to create or adjust existing security
controls to ensure they are adequate for risk mitigation needs. When adjusting the
controls to mitigate the risks, how often should the CISO perform an audit to verify
the controls?
A. Annually
B. Semi-annually
C. Quarterly
D. Never
Answer: D
QUESTION: 335
The process for management approval of the security certification process which
states the risks and mitigation of such risks of a given IT system is called
A. Security certification
B. Security system analysis
106
C. Security accreditation
D. Alignment with business practices and goals.
Answer: C
QUESTION: 336
Scenario: Your program is developed around minimizing risk to information by
focusing on people, technology, and operations. You have decided to deal with risk to
information from people first. How can you minimize risk to your most sensitive
information before granting access?
A. Conduct background checks on individuals before hiring them
B. Develop an Information Security Awareness program
C. Monitor employee browsing and surfing habits
D. Set your firewall permissions aggressively and monitor logs regularly.
Answer: A
QUESTION: 337
Scenario: The new CISO was informed of all the Information Security projects that
the section has in progress. Two projects are over a year behind schedule and way
over budget. Using the best business practices for project management, you determine
that the project correctly aligns with the organization goals. What should be verified
next?
A. Scope
B. Budget
C. Resources
D. Constraints
Answer: A
QUESTION: 338
What are the primary reasons for the development of a business case for a security
project?
A. To estimate risk and negate liability to the company
B. To understand the attack vectors and attack sources
107
C. To communicate risk and forecast resource needs
D. To forecast usage and cost per software licensing
Answer: C
QUESTION: 339
File Integrity Monitoring (FIM) is considered a
A. Network based security preventative control
B. Software segmentation control
C. Security detective control
D. User segmentation control
Answer: C
QUESTION: 340
Scenario: As you begin to develop the program for your organization, you assess the
corporate culture and determine that there is a pervasive opinion that the security
program only slows things down and limits the performance of the �real workers.�
What must you do first in order to shift the prevailing opinion and reshape corporate
culture to understand the value of information security to the organization?
A. Cite compliance with laws, statutes, and regulations � explaining the financial
implications for the company for non-compliance
B. Understand the business and focus your efforts on enabling operations securely
C. Draw from your experience and recount stories of how other companies have been
compromised
D. Cite corporate policy and insist on compliance with audit findings
Answer: B
QUESTION: 341
Acceptable levels of information security risk tolerance in an organization should be
determined by?
A. Corporate legal counsel
B. CISO with reference to the company goals
C. CEO and board of director
108
D. Corporate compliance committee
Answer: C
QUESTION: 342
When dealing with risk, the information security practitioner may choose to:
A. assign
B. transfer
C. acknowledge
D. defer
Answer: C
QUESTION: 343
Scenario: Your organization employs single sign-on (user name and password only)
as a convenience to your employees to access organizational systems and data.
Permission to individual systems and databases is vetted and approved through
supervisors and data owners to ensure that only approved personnel can use particular
applications or retrieve information. All employees have access to their own human
resource information, including the ability to change their bank routing and account
information and other personal details through the Employee Self-Service application.
All employees have access to the organizational VPN. What type of control is being
implemented by supervisors and data owners?
A. Management
B. Operational
C. Technical
D. Administrative
Answer: B
109
KILLEXAMS.COM
Killexams.com is a leading online platform specializing in high-quality certification
exam preparation. Offering a robust suite of tools, including MCQs, practice tests,
and advanced test engines, Killexams.com empowers candidates to excel in their
certification exams. Discover the key features that make Killexams.com the go-to
choice for exam success.
Exam Questions:
Killexams.com provides exam questions that are experienced in test centers. These questions are
updated regularly to ensure they are up-to-date and relevant to the latest exam syllabus. By
studying these questions, candidates can familiarize themselves with the content and format of
the real exam.
Exam MCQs:
Killexams.com offers exam MCQs in PDF format. These questions contain a comprehensive
collection of questions and answers that cover the exam topics. By using these MCQs, candidate
can enhance their knowledge and improve their chances of success in the certification exam.
Practice Test:
Killexams.com provides practice test through their desktop test engine and online test engine.
These practice tests simulate the real exam environment and help candidates assess their
readiness for the actual exam. The practice test cover a wide range of questions and enable
candidates to identify their strengths and weaknesses.
Guaranteed Success:
Killexams.com offers a success guarantee with the exam MCQs. Killexams claim that by using this
materials, candidates will pass their exams on the first attempt or they will get refund for the
purchase price. This guarantee provides assurance and confidence to individuals preparing for
certification exam.
Updated Contents:
Killexams.com regularly updates its question bank of MCQs to ensure that they are current and
reflect the latest changes in the exam syllabus. This helps candidates stay up-to-date with the exam
content and increases their chances of success.
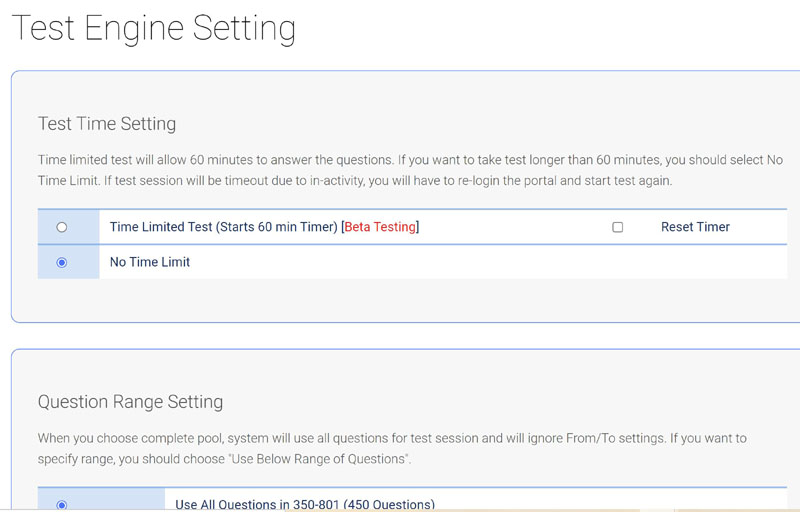
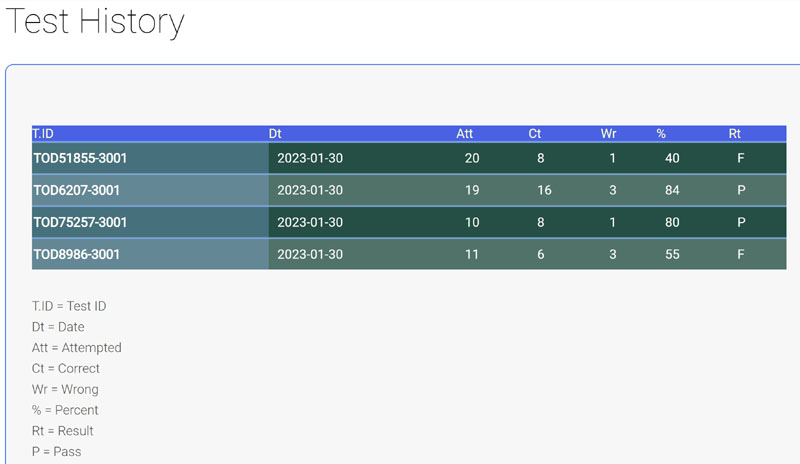
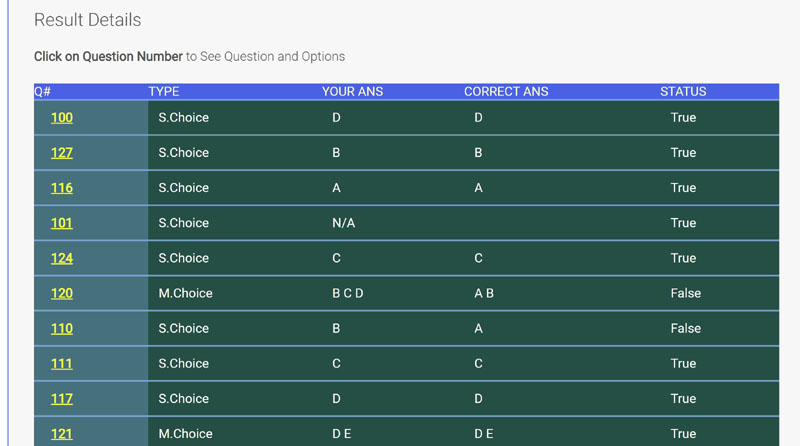
Killexams has introduced Online Test Engine (OTE) that supports iPhone, iPad, Android, Windows and Mac. 712-50 Online Testing system will helps you to study and practice using any device. Our OTE provide all features to help you memorize and practice test questions and answers while you are travelling or visiting somewhere. It is best to Practice 712-50 MCQs so that you can answer all the questions asked in test center. Our Test Engine uses Questions and Answers from Actual EC-Council Certified CISO (CCISO) exam.
Killexams.com provides the latest and most advanced version of Killexams EC-Council Certified CISO (CCISO) MCQs, incorporating MCQs and exam questions for the most recent topics of the EC-Council 712-50 Exam. Our authentic 712-50 MCQs Practice Test program will elevate your expertise and ensure you excel in your 712-50 exam with outstanding results. We guarantee your triumph at the Test Center, thoroughly addressing all exam topics and enhancing your mastery of the 712-50 exam. Achieve success with confidence using our precise questions, suppo
For a fast and effective path to passing the EC-Council 712-50 exam, killexams.com provides authentic 712-50 Practice Test Questions and Solutions in two versatile formats: 712-50 PDF and 712-50 VCE test simulator. Our 712-50 free questions PDF is accessible on any device and can be printed for convenient reference, boasting an impressive 98.9% pass rate that has empowered countless candidates to succeed in the 712-50 exam. At killexams.com, we deliver the most current and dependable 712-50 examcollection Practice Tests, meticulously covering all 712-50 exam objectives, organized by topic. Our PDF and VCE Exam Simulator versions of Questions and Answers replicate the real EC-Council 712-50 exam environment, ensuring an immersive preparation experience. With our 712-50 practice questions and Solutions, you can efficiently absorb critical information, bypassing the need for time-consuming reference books. Start your journey to certification success with killexams.com today.
712-50 Practice Questions, 712-50 study guides, 712-50 Questions and Answers, 712-50 Free PDF, 712-50 TestPrep, Pass4sure 712-50, 712-50 Practice Test, Download 712-50 Practice Questions, Free 712-50 pdf, 712-50 Question Bank, 712-50 Real Questions, 712-50 Mock Test, 712-50 Bootcamp, 712-50 Download, 712-50 VCE, 712-50 Test Engine
I am proud to have scored 89% on the challenging 712-50 exam, thanks to killexams.com accurate exam questions assessments. Their resources thoroughly evaluated my capabilities, ensuring I was well-prepared. This platform is ideal for exams taken close to academic deadlines, offering reliable updates and support.
Shahid nazir [2026-6-17]
The Killexams.com practice tests with exam dumps and exam simulator were crucial to my success in passing the 712-50 exam on my first attempt. The workbook-style questions allowed me to apply my knowledge effectively, while the simulator provided a realistic preview of the exam format. I am immensely grateful for these tools, which made my preparation both thorough and enjoyable.
Shahid nazir [2026-6-27]
I am ecstatic to have passed my 712-50 exam exam with a 97% score, thanks to killexams.com crucial exam questions exam simulator and study materials. Their resources were pivotal to my success, and I wholeheartedly thank them for their outstanding support.
Lee [2026-6-20]
More 712-50 testimonials...
EC-Council Certified CISO (CCISO) TestPrep
EC-Council Certified CISO (CCISO) Mock Exam
EC-Council Certified CISO (CCISO) free test prep
EC-Council Certified CISO (CCISO) TestPrep
EC-Council Certified CISO (CCISO) Practice Test
EC-Council Certified CISO (CCISO) Free PDF
EC-Council Certified CISO (CCISO) Mock Exam
EC-Council Certified CISO (CCISO) Mock Exam
What happens if I fail the 712-50 exam?
First of all, if you read and memorize all 712-50 practice questions and practice with the VCE exam simulator, you will surely pass your exam. But in case, you fail the exam you can get the new exam in replacement of the present exam or refund. You can further check details at https://killexams.com/pass-guarantee
Certainly, Killexams is 100% legit and even fully reputable. There are several characteristics that makes killexams.com genuine and straight. It provides current and 100 percent valid exam dumps that contain real exams questions and answers. Price is nominal as compared to a lot of the services online. The questions and answers are updated on frequent basis through most recent brain dumps. Killexams account make and product delivery is extremely fast. Document downloading can be unlimited and incredibly fast. Guidance is available via Livechat and Contact. These are the characteristics that makes killexams.com a sturdy website that supply exam dumps with real exams questions.
712-50 - EC-Council Certified CISO (CCISO) real questions
712-50 - EC-Council Certified CISO (CCISO) PDF Dumps
712-50 - EC-Council Certified CISO (CCISO) Free Exam PDF
712-50 - EC-Council Certified CISO (CCISO) Exam dumps
712-50 - EC-Council Certified CISO (CCISO) real questions
712-50 - EC-Council Certified CISO (CCISO) Question Bank
712-50 - EC-Council Certified CISO (CCISO) Exam Cram
712-50 - EC-Council Certified CISO (CCISO) Exam Questions
712-50 - EC-Council Certified CISO (CCISO) Actual Questions
712-50 - EC-Council Certified CISO (CCISO) test
712-50 - EC-Council Certified CISO (CCISO) information search
712-50 - EC-Council Certified CISO (CCISO) guide
712-50 - EC-Council Certified CISO (CCISO) study tips
712-50 - EC-Council Certified CISO (CCISO) Exam Cram
712-50 - EC-Council Certified CISO (CCISO) Exam Questions
712-50 - EC-Council Certified CISO (CCISO) guide
712-50 - EC-Council Certified CISO (CCISO) test prep
712-50 - EC-Council Certified CISO (CCISO) outline
712-50 - EC-Council Certified CISO (CCISO) learning
712-50 - EC-Council Certified CISO (CCISO) test
712-50 - EC-Council Certified CISO (CCISO) braindumps
712-50 - EC-Council Certified CISO (CCISO) braindumps
712-50 - EC-Council Certified CISO (CCISO) certification
712-50 - EC-Council Certified CISO (CCISO) cheat sheet
712-50 - EC-Council Certified CISO (CCISO) exam syllabus
712-50 - EC-Council Certified CISO (CCISO) tricks
712-50 - EC-Council Certified CISO (CCISO) study tips
712-50 - EC-Council Certified CISO (CCISO) exam
712-50 - EC-Council Certified CISO (CCISO) techniques
712-50 - EC-Council Certified CISO (CCISO) Question Bank
712-50 - EC-Council Certified CISO (CCISO) information hunger
712-50 - EC-Council Certified CISO (CCISO) PDF Questions
712-50 - EC-Council Certified CISO (CCISO) exam
712-50 - EC-Council Certified CISO (CCISO) exam syllabus
712-50 - EC-Council Certified CISO (CCISO) PDF Dumps
712-50 - EC-Council Certified CISO (CCISO) tricks
712-50 - EC-Council Certified CISO (CCISO) certification
712-50 - EC-Council Certified CISO (CCISO) outline
712-50 - EC-Council Certified CISO (CCISO) test
712-50 - EC-Council Certified CISO (CCISO) Latest Topics
712-50 - EC-Council Certified CISO (CCISO) PDF Dumps
712-50 - EC-Council Certified CISO (CCISO) braindumps
712-50 - EC-Council Certified CISO (CCISO) Exam Cram
712-50 - EC-Council Certified CISO (CCISO) Latest Questions
Prepare smarter and pass your exams on the first attempt with Killexams.com – the trusted source for authentic exam questions and answers. We provide updated and verified practice test questions, study guides, and PDF exam dumps that match the actual exam format. Unlike many other websites that resell outdated material, Killexams.com ensures daily updates and accurate content written and reviewed by certified experts.
Download real exam questions in PDF format instantly and start preparing right away. With our Premium Membership, you get secure login access delivered to your email within minutes, giving you unlimited downloads of the latest questions and answers. For a real exam-like experience, practice with our VCE Exam Simulator, track your progress, and build 100% exam readiness.
Join thousands of successful candidates who trust Killexams.com for reliable exam preparation. Sign up today, access updated materials, and boost your chances of passing your exam on the first try!
Below are some important links for test taking candidates
Medical Exams
Financial Exams
Language Exams
Entrance Tests
Healthcare Exams
Quality Assurance Exams
Project Management Exams
Teacher Qualification Exams
Banking Exams
Request an Exam
Search Any Exam