PECB Certified ISO/IEC 27001 Lead Auditor Practice Test


Exam Specification: ISO-IEC-27001-Lead-Auditor (PECB Certified ISO/IEC 27001 Lead Auditor)
Exam Name: ISO-IEC-27001-Lead-Auditor (PECB Certified ISO/IEC 27001 Lead Auditor)
Exam Code: ISO-IEC-27001-Lead-Auditor
Exam Duration: 3 hours
Passing Score: Not specified
Exam Format: Multiple-choice
Course Outline:
1. Introduction to Information Security Management Systems (ISMS)
- Understanding the principles and concepts of information security
- Overview of ISO/IEC 27001 and its requirements
- Roles and responsibilities of an ISMS lead auditor
2. Planning and Initiating an ISO/IEC 27001 Audit
- Establishing the audit objectives- scope- and criteria
- Developing an audit plan and schedule
- Conducting the opening meeting with auditees
3. Conducting an ISO/IEC 27001 Audit
- Gathering and evaluating audit evidence
- Interviewing auditees and conducting site visits
- Documenting audit findings and observations
4. Audit Reporting and Communication
- Preparing and issuing an audit report
- Communicating audit findings to relevant stakeholders
- Addressing corrective actions and follow-up activities
5. Audit Follow-up and Closure
- Evaluating the effectiveness of corrective actions
- Verifying compliance with ISO/IEC 27001 requirements
- Finalizing the audit and preparing for closure
Exam Objectives:
1. Understand the principles and concepts of information security management.
2. Familiarize oneself with the ISO/IEC 27001 standard and its requirements.
3. Plan and initiate an ISO/IEC 27001 audit effectively.
4. Conduct an ISO/IEC 27001 audit- including gathering and evaluating audit evidence.
5. Report audit findings and communicate them to relevant stakeholders.
6. Follow up on audit findings and verify the effectiveness of corrective actions.
7. Close the audit process and ensure compliance with ISO/IEC 27001 requirements.
Exam Syllabus:
Section 1: Introduction to Information Security Management Systems (10%)
- Information security principles and concepts
- Overview of ISO/IEC 27001 and its requirements
- Role of an ISMS lead auditor
Section 2: Planning and Initiating an ISO/IEC 27001 Audit (20%)
- Audit objectives- scope- and criteria
- Development of an audit plan and schedule
- Conducting the opening meeting with auditees
Section 3: Conducting an ISO/IEC 27001 Audit (40%)
- Gathering and evaluating audit evidence
- Interviewing auditees and conducting site visits
- Documentation of audit findings and observations
Section 4: Audit Reporting and Communication (15%)
- Preparation and issuance of an audit report
- Communication of audit findings to stakeholders
- Addressing corrective actions and follow-up activities
Section 5: Audit Follow-up and Closure (15%)
- Evaluation of corrective actions' effectiveness
- Verification of compliance with ISO/IEC 27001 requirements
- Finalization of the audit and closure
Complete Exam Objectives:
-------------------------
- Domain 1: Fundamental principles and concepts of an information security management system (ISMS)
- understand and explain the main concepts of the information security management system
- understand and explain the organization’s operations and the development of information security standards
- identify- analyze- and evaluate the information security compliance requirements for an organization
- explain and illustrate the main concepts in information security and information security risk management
- distinguish and explain the difference between information asset- data and record
- understand- interpret- and illustrate the relationship between information security aspects such as controls- vulnerabilities- threats- risks- and assets
- illustrate big data- artificial intelligence- machine learning- cloud computing- and outsourcing operations
- Domain 2: Information security management system (ISMS)
- understanding the ISO/IEC 27001 requirements and the structure of the standard
- understanding the components of an information security management system based on ISO/IEC 27001 and its principal processes
- understand- interpret- and analyze the requirements of ISO/IEC 27001
- understanding whether the organization has satisfied the needs of the interested parties
- understand- explain- and illustrate the main steps to establish- implement- operate- monitor- review- maintain- and improve an organization’s ISMS
- understanding the risk assessment approach and methodology
- understanding the selection of appropriate controls based upon Annex A of ISO/IEC 27001
- Domain 3: Fundamental audit concepts and principles
- understand- explain- and illustrate the application of the audit principles in an ISMS audit
- differentiate first- second- and third party audits
- identify and judge situations that would discredit the professionalism of the auditor and violate the PECB Code of Ethics
- identify and judge ethical issues considering the obligations related to the audit client- auditee- law enforcement- and regulatory authorities
- understanding the legal implications related to any irregularities committed by the auditee
- understanding the impact of trends and technology in auditing
- explain- illustrate- and apply the audit evidence approach in the context of an ISMS audit
- explain and compare evidence types and their characteristics
- determine and justify the type and amount of evidence required in an ISMS audit
- Domain 4: Preparing an ISO/IEC 27001 audit
- determine and evaluate the level of materiality and apply the risk-based approach during the different stages of an ISMS audit
- judge the appropriate level of reasonable assurance needed for an ISMS audit
- understand and illustrate the steps and activities to prepare an ISMS audit considering the specific context of the audit
- understand and explain the roles and responsibilities of the audit team leader- audit team members- and technical experts
- determine and evaluate the level of materiality during the different stages of an ISMS audit
- determine the audit feasibility
- determine- evaluate- and confirm the audit objectives- the audit criteria- and the audit scope for an ISMS audit
- explain- illustrate- and define the characteristics of the terms of the audit engagement and apply the best practices to establish the initial contact with an auditee
- Domain 5: Conducting an ISO/IEC 27001 audit
- conduct the stage 1 audit- taking into account the documented information evaluation criteria
- organize and conduct an opening meeting
- conduct the stage 2 audit by appropriately following the procedures that this stage entails
- apply the best practices of communication to collect the appropriate audit evidence
- consider the roles and responsibilities of all the interested parties involved
- explain- illustrate- and apply evidence collection procedures and tools
- explain- illustrate- and apply the main audit sampling methods
- gather appropriate evidence from the available information during an audit and evaluate it objectively
- explain- illustrate- and apply the audit evidence approach in an ISMS audit
- develop audit working papers and elaborate appropriate audit test plans in an ISMS audit
- explain and apply the evidence evaluation process: drafting audit findings
- understand- explain- and illustrate the concept of the benefit of the doubt
- report appropriate audit observations in accordance with audit rules and principles
- conduct quality reviews to audit documentation
- complete audit working documents
- Domain 6: Closing an ISO/IEC 27001 audit
- explain and apply the evidence evaluation process: preparing audit conclusions
- justify the recommendation for certification
- draft and present audit conclusions
- organize and conduct a closing meeting
- write and distribute an ISO/IEC 27001 audit report
- evaluate action plans
- Domain 7: Managing an ISO/IEC 27001 audit program
- conduct the activities following an initial audit- including audit follow-ups and surveillance activities
- understand and explain the establishment of an audit program and the application of the PDCA cycle into an audit program
- understand and explain the importance of protecting the integrity- availability- and confidentiality of audit records and the auditors’ responsibilities in this regard
- understand and explain the responsibilities to protect the integrity- availability and confidentiality of audit records
- understand the requirements related to the components of the management system of an audit program as quality management- record management- complaint management
- understand and explain the way that the combined audits are handled in an audit program
- understand the documented information management process
- understand the process of evaluating the efficiency of the audit program by monitoring the performance of each auditor and audit team member
- demonstrate the application of the personal attributes and behaviors associated with professional auditors

ISO-IEC-27001-Lead-Auditor MCQs
ISO-IEC-27001-Lead-Auditor TestPrep
ISO-IEC-27001-Lead-Auditor Study Guide
ISO-IEC-27001-Lead-Auditor Practice Test
ISO-IEC-27001-Lead-Auditor Exam Questions
killexams.com
PECB
ISO-IEC-27001-Lead-Auditor
PECB Certified ISO/IEC 27001 Lead Auditor 2026
https://killexams.com/pass4sure/exam-detail/ISO-IEC-27001-Lead-Auditor
Question: 559
In the context of security incident management, what does the term "escalation" refer to?
A. The initial reporting of a security incident
B. The documentation of security incidents
C. The process of increasing the urgency of a response
D. The analysis of the root cause of an incident
Answer: C
Explanation: Escalation in security incident management refers to increasing the urgency of a response,
often involving notifying higher levels of management or specialized teams when a security incident
occurs.
Question: 560
While reviewing audit documentation, you realize that the evidence collected does not adequately
substantiate the conclusions drawn in the audit report. What is the best course of action?
A. Revise the audit conclusions to fit the available evidence
B. Present the findings as they are without modification
C. Ignore the discrepancies as they do not affect the overall audit
D. Document the inadequacies and suggest further investigation
Answer: D
Explanation: Documenting inadequacies and suggesting further investigation ensures that the audit report
is accurate, reliable, and reflective of the true state of the ISMS.
Question: 561
As you conduct a stage 2 audit, you find that the organization has not implemented some of the controls
as stated in their ISMS documentation. Which action should you take first?
A. Verify with relevant personnel why the controls were not implemented
B. Discuss your findings with the audit team
C. Prepare a non-conformity report immediately
D. Suggest additional controls to mitigate the risks
Answer: A
Explanation: It is crucial to understand why the controls were not implemented before concluding they
are non-conformities. This step ensures that you gather adequate evidence and context regarding the
organization's practices.
Question: 562
In an ISMS audit, which type of evidence is most valuable when assessing the effectiveness of the risk
treatment plan, and what characteristics make this evidence preferable?
A. Testimonial evidence from management due to its authority.
B. Physical evidence, as it is tangible and verifiable.
C. Circumstantial evidence, as it supports the overall context.
D. Documentary evidence, which provides a clear trail of actions taken.
Answer: D
Explanation: Documentary evidence is crucial in assessing the effectiveness of a risk treatment plan since
it provides a clear, verifiable record of actions taken and decisions made, ensuring transparency and
accountability.
Question: 563
Which document serves as the foundation for developing an ISMS in compliance with ISO/IEC 27001?
A. Risk assessment report
B. Business continuity plan
C. Incident management plan
D. Information security policy
Answer: D
Explanation: The information security policy serves as the foundation for developing an ISMS, outlining
the organization�s approach to managing information security.
Question: 564
What is the primary challenge an auditor faces when determining the amount of evidence required for an
ISMS audit, particularly in relation to varying organizational contexts?
A. There is a standard amount of evidence that applies to all organizations.
B. The auditor must account for the specific risks and complexities of the organization.
C. Evidence requirements are solely based on the auditor's preferences.
D. Organizations typically provide an excessive amount of evidence.
Answer: B
Explanation: The auditor must consider the specific risks, complexities, and unique context of the
organization to determine the appropriate amount of evidence needed, as there is no one-size-fits-all
approach.
Question: 565
What is a primary reason for implementing a security awareness training program?
A. To comply with industry regulations
B. To educate employees about security risks and best practices
C. To improve employee morale
D. To reduce IT support costs
Answer: B
Explanation: A security awareness training program educates employees about security risks and best
practices, helping to mitigate human-related security incidents.
Question: 566
When evaluating the value of data, which of the following factors is MOST critical in determining its
potential impact on the organization if compromised?
A. The encryption strength used to protect the data.
B. The existence of backups for the data.
C. The sensitivity and confidentiality of the data.
D. The physical location of the data storage.
Answer: C
Explanation: The sensitivity and confidentiality of the data are crucial in assessing its value and the
potential impact on the organization if it is compromised.
Question: 567
What is the primary purpose of conducting a "Context of the Organization" analysis before establishing
an ISMS?
A. To identify resources available for information security
B. To evaluate the organization's current risk management practices
C. To understand external and internal factors affecting information security
D. To define the scope of the ISMS
Answer: C
Explanation: Understanding the context of the organization involves analyzing external and internal
factors that can impact information security, which is essential for effective ISMS establishment.
Question: 568
When evaluating ethical dilemmas in an ISMS audit, which of the following obligations must the auditor
prioritize to maintain integrity and compliance with the PECB Code of Ethics?
A. The auditor should prioritize the interests of the audit client over the requirements of regulatory
authorities.
B. The auditor must balance the interests of the auditee while ensuring compliance with legal and
regulatory obligations.
C. The auditor should focus solely on the auditee's perspective, disregarding any external regulations.
D. The auditor�s primary responsibility is to the certification body, regardless of the auditee�s compliance
status.
Answer: B
Explanation: The auditor must balance the interests of the auditee with the legal and regulatory
obligations to maintain integrity, ensuring that all parties are treated fairly and ethically.
Question: 569
Which of the following is NOT a recommended practice for ensuring data integrity in electronic records?
A. Regular audits of data access logs
B. Use of unverified third-party software
C. Implementing strict access controls
D. Maintaining a comprehensive backup strategy
Answer: B
Explanation: Using unverified third-party software can introduce vulnerabilities and risks that
compromise data integrity, making it a practice to avoid.
Question: 570
Which of the following is a key benefit of implementing a formal ISMS based on ISO/IEC 27001
standards?
A. Elimination of all security risks
B. Improved stakeholder confidence and trust in the organization
C. Automatic compliance with all regulatory requirements
D. Guaranteed protection against data breaches
Answer: B
Explanation: Implementing a formal ISMS enhances stakeholder confidence and trust by demonstrating
the organization's commitment to managing information security effectively.
Question: 571
During an ISMS audit, the assessment of audit findings should primarily aim to:
A. Identify root causes and opportunities for improvement
B. Determine compliance with ISO/IEC 27001 only
C. Highlight areas where the organization has failed
D. Provide suggestions for immediate corrective actions
Answer: A
Explanation: Assessing findings with the aim of identifying root causes and improvement opportunities
fosters a constructive audit environment that supports organizational growth.
Question: 572
In managing the audit program, you need to ensure that all auditors maintain a high level of professional
integrity. What is the best way to promote this among your audit team?
A. Provide ongoing training on ethical standards and practices
B. Implement strict penalties for unethical behavior
C. Conduct audits of auditors to monitor their performance
D. Encourage auditors to work independently without supervision
Answer: A
Explanation: Ongoing training on ethical standards reinforces the importance of integrity and equips
auditors with the knowledge to uphold these principles in their work.
Question: 573
In the context of evidence collection during an ISMS audit, how does the concept of triangulation
enhance the reliability of the findings?
A. Triangulation is irrelevant to evidence collection.
B. It combines evidence from multiple sources to confirm findings, enhancing reliability.
C. Triangulation only applies to quantitative evidence.
D. It focuses solely on subjective evidence to support findings.
Answer: B
Explanation: Triangulation enhances the reliability of findings by combining evidence from multiple
sources, allowing auditors to confirm results and reduce the risk of errors or biases in the audit process.
Question: 574
During an ISMS audit, an auditor discovers that a member of the audit team has a personal relationship
with a key stakeholder of the organization being audited. What is the most appropriate course of action
for the lead auditor?
A. Ignore the relationship as it does not directly affect the audit results.
B. Conduct the audit as planned, but document the relationship in the audit findings.
C. Allow the team member to proceed with the audit since their expertise is crucial.
D. Reassign the team member to another role within the audit team to maintain impartiality.
Answer: D
Explanation: To maintain the integrity and impartiality of the audit, the lead auditor should reassign the
team member to another role, ensuring that no conflicts of interest influence the audit process.
Question: 575
Which of the following is a common consequence of data integrity breaches in organizations?
A. Enhanced user experience
B. Legal penalties and fines
C. Improved data analytics
D. Increased customer trust
Answer: B
Explanation: Data integrity breaches can lead to legal penalties and fines, as organizations may fail to
comply with regulations governing data protection and integrity.
Question: 576
In a situation where you discover that an organization's audit records have been tampered with after an
audit, what is your immediate course of action as the lead auditor?
A. Ignore the tampering if the overall audit results are positive
B. Conclude the audit process without mentioning the tampering to avoid complications
C. Document the tampering, report it to senior management, and recommend a thorough investigation
D. Inform only the IT department, as it falls under their jurisdiction
Answer: C
Explanation: Documenting and reporting tampering is critical to maintaining the integrity of the audit
process and addressing potential compliance issues.
Question: 577
In the context of auditing practices, what challenges do auditors face when adapting to rapidly changing
technology trends, particularly in relation to evidence collection?
A. Auditors typically have sufficient training to handle all technological changes.
B. Rapid changes can lead to outdated audit techniques that may not effectively evaluate current risks.
C. Technology trends are irrelevant to auditing practices.
D. Auditors should avoid using technology altogether to maintain traditional practices.
Answer: B
Explanation: Rapid technological changes can render traditional audit techniques ineffective, creating
challenges for auditors in evaluating current risks and necessitating adaptations in their evidence
collection methods.
Question: 578
During an ISO/IEC 27001 audit, you encounter significant discrepancies between the documented
information and the actual practices observed. After the initial audit, what is the most effective approach
for conducting follow-up activities to ensure that the discrepancies are addressed in a timely manner?
A. Immediately escalate the discrepancies to senior management without further investigation
B. Ignore the discrepancies if they are minor, as they do not impact the overall audit outcome
C. Document the discrepancies and wait for the next scheduled audit cycle
D. Schedule a follow-up audit to verify corrective actions after a predefined period
Answer: D
Explanation: A follow-up audit allows for the verification of corrective actions taken to address
discrepancies, ensuring compliance and continuous improvement.
Question: 579
In the context of preparing for an ISO/IEC 27001 audit, which of the following actions is most critical for
determining the level of materiality and applying a risk-based approach during the audit stages?
A. Conducting a comprehensive review of the organization�s financial statements
B. Mapping the organization's information assets and their associated risks
C. Analyzing historical audit findings to identify recurring issues
D. Engaging in stakeholder interviews to assess their perception of risk
Answer: B
Explanation: Mapping information assets and their risks is essential for understanding the potential
impact of different audit findings and prioritizing audit activities based on risk levels.
KILLEXAMS.COM
Killexams.com is a leading online platform specializing in high-quality certification
exam preparation. Offering a robust suite of tools, including MCQs, practice tests,
and advanced test engines, Killexams.com empowers candidates to excel in their
certification exams. Discover the key features that make Killexams.com the go-to
choice for exam success.
Exam Questions:
Killexams.com provides exam questions that are experienced in test centers. These questions are
updated regularly to ensure they are up-to-date and relevant to the latest exam syllabus. By
studying these questions, candidates can familiarize themselves with the content and format of
the real exam.
Exam MCQs:
Killexams.com offers exam MCQs in PDF format. These questions contain a comprehensive
collection of questions and answers that cover the exam topics. By using these MCQs, candidate
can enhance their knowledge and improve their chances of success in the certification exam.
Practice Test:
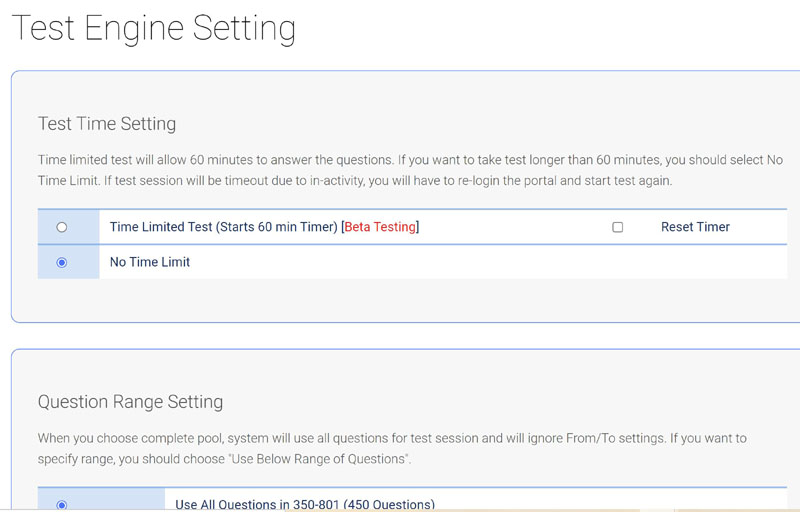
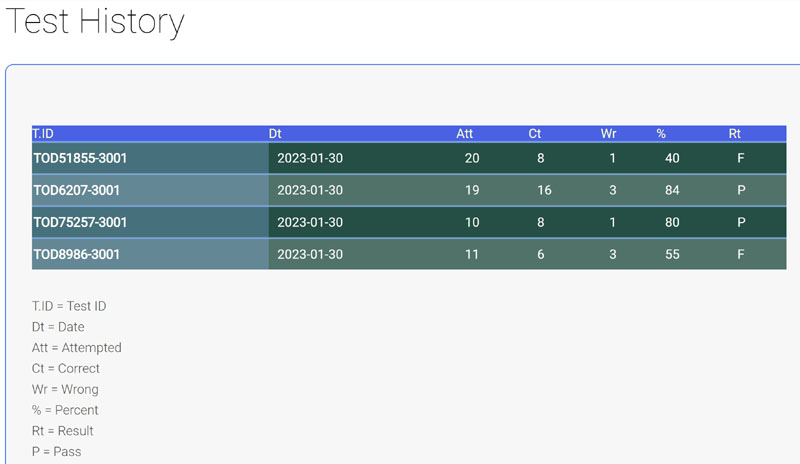
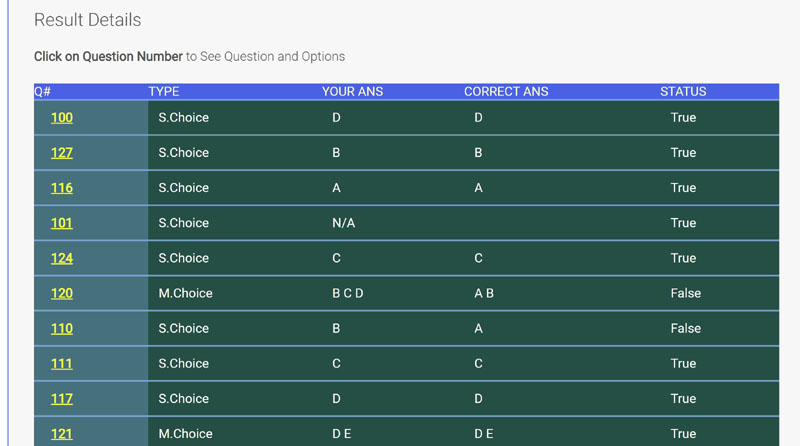
Killexams.com provides practice test through their desktop test engine and online test engine.
These practice tests simulate the real exam environment and help candidates assess their
readiness for the actual exam. The practice test cover a wide range of questions and enable
candidates to identify their strengths and weaknesses.
Guaranteed Success:
Killexams.com offers a success guarantee with the exam MCQs. Killexams claim that by using this
materials, candidates will pass their exams on the first attempt or they will get refund for the
purchase price. This guarantee provides assurance and confidence to individuals preparing for
certification exam.
Updated Contents:
Killexams.com regularly updates its question bank of MCQs to ensure that they are current and
reflect the latest changes in the exam syllabus. This helps candidates stay up-to-date with the exam
content and increases their chances of success.
Killexams has introduced Online Test Engine (OTE) that supports iPhone, iPad, Android, Windows and Mac. ISO-IEC-27001-Lead-Auditor Online Testing system will helps you to study and practice using any device. Our OTE provide all features to help you memorize and practice test questions and answers while you are travelling or visiting somewhere. It is best to Practice ISO-IEC-27001-Lead-Auditor MCQs so that you can answer all the questions asked in test center. Our Test Engine uses Questions and Answers from Actual PECB Certified ISO/IEC 27001 Lead Auditor exam.
Proven Success Stories from Satisfied PECB PECB Certified ISO/IEC 27001 Lead Auditor Exam Candidates Every single day, we receive enthusiastic success reports from candidates who have aced the PECB PECB Certified ISO/IEC 27001 Lead Auditor real exam with outstanding scores. Many are so thrilled with their results that they immediately return to killexams.com to prepare for multiple additional certifications. This overwhelming response fills us with tremendous pride, as it confirms we are fulfilling our mission: ✅ Empowering professionals to expand their knowledge ✅
Achieving success in the PECB ISO-IEC-27001-Lead-Auditor exam requires more than just studying the course guide. At killexams.com, we provide free PDF sample questions to help you practice with authentic PECB Certified ISO/IEC 27001 Lead Auditor questions and scenarios. Once confident with our material, register to download the full version of ISO-IEC-27001-Lead-Auditor prep questions Practice Tests at exclusive discounts, marking your first step toward excelling in the PECB Certified ISO/IEC 27001 Lead Auditor exam. To further enhance your expertise, install our ISO-IEC-27001-Lead-Auditor VCE exam simulator, available as both online and desktop test engines, and practice consistently with our ISO-IEC-27001-Lead-Auditor free questions Practice Tests. When prepared for the actual ISO-IEC-27001-Lead-Auditor exam, register at a test center and take the real test. Our approach goes beyond merely passing the ISO-IEC-27001-Lead-Auditor exam with our questions and answers; it focuses on deepening your understanding of ISO-IEC-27001-Lead-Auditor concepts and objectives. We are proud that countless individuals have leveraged our resources to pass the ISO-IEC-27001-Lead-Auditor exam and now thrive in rewarding roles within their organizations. Their success stems not only from studying our ISO-IEC-27001-Lead-Auditor Free PDF Practice Tests but from acquiring the knowledge and skills to excel in professional environments. Let killexams.com guide you to success as well.
ISO-IEC-27001-Lead-Auditor Practice Questions, ISO-IEC-27001-Lead-Auditor study guides, ISO-IEC-27001-Lead-Auditor Questions and Answers, ISO-IEC-27001-Lead-Auditor Free PDF, ISO-IEC-27001-Lead-Auditor TestPrep, Pass4sure ISO-IEC-27001-Lead-Auditor, ISO-IEC-27001-Lead-Auditor Practice Test, Download ISO-IEC-27001-Lead-Auditor Practice Questions, Free ISO-IEC-27001-Lead-Auditor pdf, ISO-IEC-27001-Lead-Auditor Question Bank, ISO-IEC-27001-Lead-Auditor Real Questions, ISO-IEC-27001-Lead-Auditor Mock Test, ISO-IEC-27001-Lead-Auditor Bootcamp, ISO-IEC-27001-Lead-Auditor Download, ISO-IEC-27001-Lead-Auditor VCE, ISO-IEC-27001-Lead-Auditor Test Engine
After failing my ISO-IEC-27001-Lead-Auditor exam, I was disheartened until I discovered killexams.com. Their preparation pack, including practice questions, answers, and an exam simulator, helped me identify my weaknesses and prepare effectively. I scored an impressive 98% on my next attempt, and I am deeply grateful to the killexams.com team for their invaluable support.
Lee [2026-6-15]
I passed the ISO-IEC-27001-Lead-Auditor exam this month, thanks to the excellent training questions and answers provided by Killexams.com. I can confidently vouch for the dependability of this website. Initially, I did not think that practice tests of exam questions could be this helpful, but after using Killexams.com, I realized that it offers more than just a quick sell-off. It provides you with the essential resources you need to pass your ISO-IEC-27001-Lead-Auditor exam and also enables you to learn the concepts you will truly need. It is the perfect solution for saving time and energy. I highly recommend Killexams.com to everyone.
Martin Hoax [2026-4-11]
Excellent exam questions materials were key to my passing the ISO-IEC-27001-Lead-Auditor exam exam. killexams practice tests with exam dumps and study guides provided top-notch preparation, boosting my knowledge and ensuring my success with confidence.
Martin Hoax [2026-6-18]
More ISO-IEC-27001-Lead-Auditor testimonials...
I want to talk to ISO-IEC-27001-Lead-Auditor exam expert, where should I contact?
You can send your query to [email protected] to contact our certification experts. You should expect a little longer to get a response because our team has to handle hundreds of queries in the queue. Write your query in detail with your username (if available).
Without a doubt, Killexams is fully legit and even fully trusted. There are several benefits that makes killexams.com reliable and authentic. It provides current and totally valid exam dumps made up of real exams questions and answers. Price is small as compared to the vast majority of services online. The questions and answers are updated on frequent basis having most recent brain dumps. Killexams account arrangement and device delivery is amazingly fast. Data downloading is certainly unlimited and very fast. Assistance is available via Livechat and Email. These are the characteristics that makes killexams.com a sturdy website that come with exam dumps with real exams questions.
ISO-IEC-27001-Lead-Auditor - PECB Certified ISO/IEC 27001 Lead Auditor testing
ISO-IEC-27001-Lead-Auditor - PECB Certified ISO/IEC 27001 Lead Auditor Exam Cram
ISO-IEC-27001-Lead-Auditor - PECB Certified ISO/IEC 27001 Lead Auditor information hunger
ISO-IEC-27001-Lead-Auditor - PECB Certified ISO/IEC 27001 Lead Auditor Actual Questions
ISO-IEC-27001-Lead-Auditor - PECB Certified ISO/IEC 27001 Lead Auditor Study Guide
ISO-IEC-27001-Lead-Auditor - PECB Certified ISO/IEC 27001 Lead Auditor PDF Braindumps
ISO-IEC-27001-Lead-Auditor - PECB Certified ISO/IEC 27001 Lead Auditor information source
ISO-IEC-27001-Lead-Auditor - PECB Certified ISO/IEC 27001 Lead Auditor exam dumps
ISO-IEC-27001-Lead-Auditor - PECB Certified ISO/IEC 27001 Lead Auditor exam
ISO-IEC-27001-Lead-Auditor - PECB Certified ISO/IEC 27001 Lead Auditor exam
ISO-IEC-27001-Lead-Auditor - PECB Certified ISO/IEC 27001 Lead Auditor Study Guide
ISO-IEC-27001-Lead-Auditor - PECB Certified ISO/IEC 27001 Lead Auditor outline
ISO-IEC-27001-Lead-Auditor - PECB Certified ISO/IEC 27001 Lead Auditor PDF Download
ISO-IEC-27001-Lead-Auditor - PECB Certified ISO/IEC 27001 Lead Auditor Exam Questions
ISO-IEC-27001-Lead-Auditor - PECB Certified ISO/IEC 27001 Lead Auditor exam dumps
ISO-IEC-27001-Lead-Auditor - PECB Certified ISO/IEC 27001 Lead Auditor learning
ISO-IEC-27001-Lead-Auditor - PECB Certified ISO/IEC 27001 Lead Auditor learn
ISO-IEC-27001-Lead-Auditor - PECB Certified ISO/IEC 27001 Lead Auditor information search
ISO-IEC-27001-Lead-Auditor - PECB Certified ISO/IEC 27001 Lead Auditor Latest Topics
ISO-IEC-27001-Lead-Auditor - PECB Certified ISO/IEC 27001 Lead Auditor Exam Questions
ISO-IEC-27001-Lead-Auditor - PECB Certified ISO/IEC 27001 Lead Auditor exam contents
ISO-IEC-27001-Lead-Auditor - PECB Certified ISO/IEC 27001 Lead Auditor Cheatsheet
ISO-IEC-27001-Lead-Auditor - PECB Certified ISO/IEC 27001 Lead Auditor Exam Braindumps
ISO-IEC-27001-Lead-Auditor - PECB Certified ISO/IEC 27001 Lead Auditor exam syllabus
ISO-IEC-27001-Lead-Auditor - PECB Certified ISO/IEC 27001 Lead Auditor Study Guide
ISO-IEC-27001-Lead-Auditor - PECB Certified ISO/IEC 27001 Lead Auditor outline
ISO-IEC-27001-Lead-Auditor - PECB Certified ISO/IEC 27001 Lead Auditor real questions
ISO-IEC-27001-Lead-Auditor - PECB Certified ISO/IEC 27001 Lead Auditor test prep
ISO-IEC-27001-Lead-Auditor - PECB Certified ISO/IEC 27001 Lead Auditor Exam Questions
ISO-IEC-27001-Lead-Auditor - PECB Certified ISO/IEC 27001 Lead Auditor certification
ISO-IEC-27001-Lead-Auditor - PECB Certified ISO/IEC 27001 Lead Auditor test
ISO-IEC-27001-Lead-Auditor - PECB Certified ISO/IEC 27001 Lead Auditor braindumps
ISO-IEC-27001-Lead-Auditor - PECB Certified ISO/IEC 27001 Lead Auditor learn
ISO-IEC-27001-Lead-Auditor - PECB Certified ISO/IEC 27001 Lead Auditor teaching
ISO-IEC-27001-Lead-Auditor - PECB Certified ISO/IEC 27001 Lead Auditor Exam dumps
ISO-IEC-27001-Lead-Auditor - PECB Certified ISO/IEC 27001 Lead Auditor tricks
ISO-IEC-27001-Lead-Auditor - PECB Certified ISO/IEC 27001 Lead Auditor Exam Questions
ISO-IEC-27001-Lead-Auditor - PECB Certified ISO/IEC 27001 Lead Auditor study tips
ISO-IEC-27001-Lead-Auditor - PECB Certified ISO/IEC 27001 Lead Auditor Latest Topics
ISO-IEC-27001-Lead-Auditor - PECB Certified ISO/IEC 27001 Lead Auditor information source
ISO-IEC-27001-Lead-Auditor - PECB Certified ISO/IEC 27001 Lead Auditor certification
ISO-IEC-27001-Lead-Auditor - PECB Certified ISO/IEC 27001 Lead Auditor PDF Braindumps
ISO-IEC-27001-Lead-Auditor - PECB Certified ISO/IEC 27001 Lead Auditor outline
ISO-IEC-27001-Lead-Auditor - PECB Certified ISO/IEC 27001 Lead Auditor guide
Prepare smarter and pass your exams on the first attempt with Killexams.com – the trusted source for authentic exam questions and answers. We provide updated and verified practice test questions, study guides, and PDF exam dumps that match the actual exam format. Unlike many other websites that resell outdated material, Killexams.com ensures daily updates and accurate content written and reviewed by certified experts.
Download real exam questions in PDF format instantly and start preparing right away. With our Premium Membership, you get secure login access delivered to your email within minutes, giving you unlimited downloads of the latest questions and answers. For a real exam-like experience, practice with our VCE Exam Simulator, track your progress, and build 100% exam readiness.
Join thousands of successful candidates who trust Killexams.com for reliable exam preparation. Sign up today, access updated materials, and boost your chances of passing your exam on the first try!
Below are some important links for test taking candidates
Medical Exams
Financial Exams
Language Exams
Entrance Tests
Healthcare Exams
Quality Assurance Exams
Project Management Exams
Teacher Qualification Exams
Banking Exams
Request an Exam
Search Any Exam